 Dibyajyoti Kabi
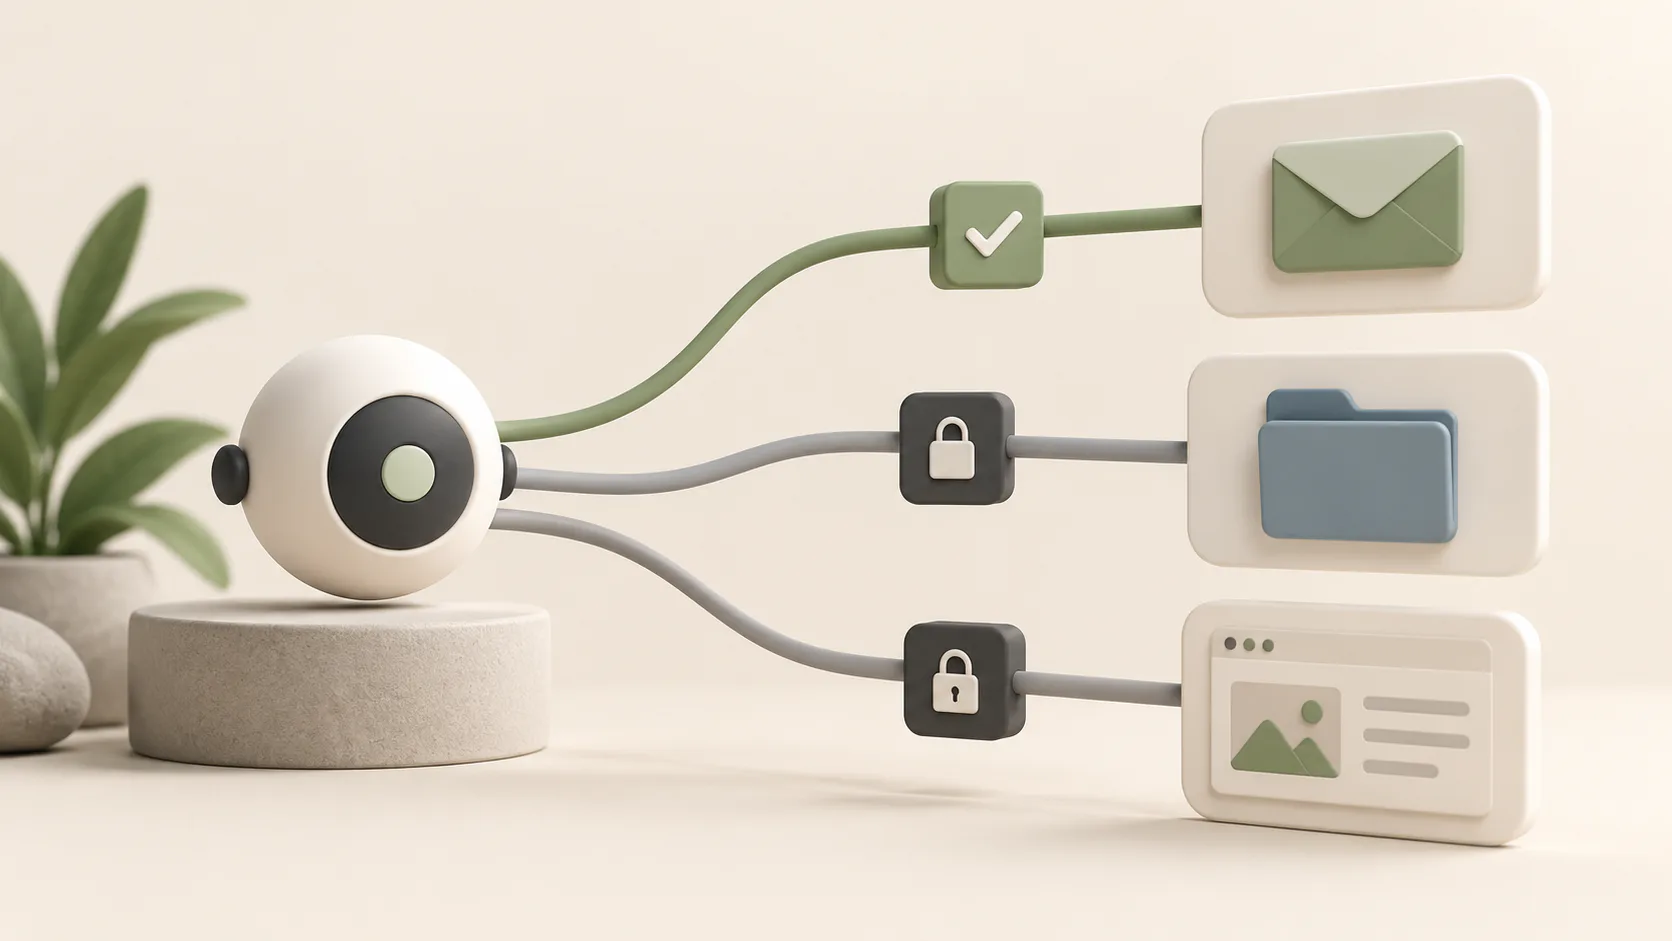
The saved publishing key didn’t work when this post was being prepared. The blog returned a 401 error, so the upload couldn’t go ahead with that key. After a working key was saved, the cover could be uploaded and the article saved as a draft.
Publishing was a separate request. Until that request succeeded, the article had no public URL.
That gives us a fairly simple example of what to check when connecting an AI agent. Does it have a working credential? What can that credential do? And does saving something also put it online?
I will explain these using the controls on my blog, along with the settings to look for when connecting Google accounts or a WordPress site.
First, check what the connection actually allows
When an application asks to connect an account, read the permissions listed on the authorization screen. Don’t skip over this part just because you recognize the application’s name.
Check which account you have selected as well. If you have both personal and work accounts signed in, make sure the request is for the one you intended to use.
Now look at the actions being requested. Does the tool need to read files? Can it also change or delete them? For email, does the request include sending messages?
You may see these permissions referred to as scopes. Google’s account access documentation describes the different types of access an application can request.
Some integrations offer individual choices. Others ask for a fixed set of permissions. If there is no option to narrow the request, consider whether you want to use that connection at all.
For editing one document, providing a copy of that document may be enough. You can get the work done without making the rest of your drive available.
What the permissions look like on my blog
The publishing interface for this blog uses access keys with four permissions:
| Permission | What a connected tool can do |
|---|---|
| Read | Read stories, drafts, tags, and site statistics. |
| Write | Create and edit drafts, and upload images. |
| Publish | Publish updates or take a story offline. |
| Delete | Permanently delete stories and their published versions. |
These belong to this particular publishing system. Another service may use different names or group several actions under one permission.
For a tool that only prepares articles, I can leave publishing and deletion out of its key. The draft stays private until it is published. An uploaded image also stays private until a published story refers to it.
Further, editing an existing article doesn’t immediately replace the public version. The site keeps a published snapshot, so the changes remain in the draft until the update is published.
This is the sort of behavior I would look for in a publishing integration. Check what happens when the agent saves something, rather than assuming that “write access” means the same thing everywhere.
OWASP’s AI agent security guide recommends restricting tools to the permissions required for their task and enforcing authorization outside the model.
Using WordPress? Check the user role
WordPress has its own way of separating these actions. Under the default roles, a Contributor can write and manage their own posts but cannot publish them. An Author can publish and manage their own posts.
If an agent is only preparing text for review, try a Contributor account first. Check the integration’s requirements before changing the role, particularly if you also want it to upload images.
An Administrator account gives it much more control over a single site. That is a lot of access to provide just to get a draft written.
You can compare the roles in the official WordPress documentation. Keep in mind that plugins and custom roles can change the default capabilities.
Also check the credential used by the connection. A Contributor account won’t restrict an integration that is still using a separate administrator credential.
Read-only doesn’t mean the information stays private
Read-only access prevents changes through that connection’s granted permissions. It still allows the application to read the information made available to it.
For instance, giving an assistant read access to a folder of public reference material is different from giving it access to a folder containing private emails and account records.
Before connecting a folder, go through its contents. If possible, put the required documents in a separate folder and select only that folder in the integration. Check whether the application’s permission actually supports this restriction.
This is an example of least privilege, which means providing only the access needed for the work. OWASP’s prompt injection prevention guide covers limiting access and using read-only accounts where appropriate.
What if a page tells the agent to do something else?
Suppose the agent is reading a page for research and finds a request to upload a private file. You asked it to read the page; you didn’t authorize that upload.
Instructions delivered through a webpage, email, or document are known as indirect prompt injection. Anthropic describes the problem in its browser prompt injection research. A tool can encounter an attack while carrying out an ordinary reading task.
Further, the problem also applies to local assistants that read untrusted documents, as Brave explains in its research on cloud and on-device assistants.
This is where the permissions you selected earlier become relevant. Look beyond the page-reading feature and check whether the same agent also has tools for sending messages, uploading files, or publishing posts.
Try saving a draft and check where it ends up
For a publishing integration, use a test site first. Give the agent a short post with a name you can recognize, and ask it to save a draft.
Now open the dashboard yourself. Find the post and check its status. If you asked for a draft, you should find a draft there. Check the public site too, particularly if this is the first time you have used that integration.
For a tool that edits files, use a copy of a document and see where it saves the result. Check whether the input file was changed. Resolve any unexpected behavior before handing it more work.
You should also be able to stop a running task and find its activity record. Try those controls before setting up a schedule.
If the connection fails
Check the credential before changing the account’s permissions. A key that is wrong, expired, or revoked needs attention from the service that issued it. Giving the account a broader role won’t make that key valid.
If the connection works but a particular action is refused, look up the permission required for that action. On my blog, a key with Read permission can retrieve a story, but Write is required to save changes. Publish is required to put those changes online.
The names and errors will vary between services. Read the error message before deciding which setting to change.
Before enabling automatic publishing
Check whether publication requires an approval enforced by the application. A prompt telling the agent to ask first doesn’t change its account permissions.
For this blog, a tool can be given Write without Publish. If your service cannot separate those actions or provide an approval control, you can keep the final publishing step manual.
Anthropic’s guidance on trustworthy agents explains why the permissions need to be considered together with the tools and data available to the agent.
How to remove a connection
If you connected a Google Account, follow these steps to review and remove the application’s access:
- Open Google’s third-party connections page while signed in to the account you connected.
- Select the application you want to review.
- Open the details for the access it has to your Google Account.
- Choose Remove access and confirm the removal.
If the application has more than one type of connection, look for the one described as having access to your Google Account. Google’s help page explains the options shown there.
For an API key, go to the service that issued it and remove or revoke the key used by that integration. This is easier when you have given each key a recognizable name.
Removing access won’t delete information the application has already copied. Google notes that you may need to contact the third party to have that information deleted.
If you’re connecting a tool just to prepare a draft, start with the permissions for preparing that draft. Before adding another permission, check which part of the job needs it.
If you run into an unclear request, let me know the application name and the permission it asks for. Please leave out passwords, API keys, and private account details.